
 Qwacks
 Flock
 Protokite
 Data Duck
- Game — the SDK authenticates your game with the credentials you configure once: the API Key, which game it is, and the Game Version. Every request it makes is then identified as your game.
- Player — players sign in through the SDK, which then manages their session automatically for the rest of play.
Configure your game
Set your credentials in your engine’s settings. The editor resolves your Game Version, which the SDK needs before it can start, and can also verify the connection for you (an optional check).- Unity
- Unreal
Credentials live in Flock → Settings, Configuration tab: Api Url, Api Key, Game Name
(your game’s name from the dashboard) and Game Version — see Unity setup.With Auto-Initialize On Load the SDK authenticates as your game at startup; turn it off to
initialize it yourself. Reach everything through
FlockClient.Instance.Sign in a player
Players sign in with one of several methods. Each resolves to the same player account, and the SDK keeps them signed in afterward.- Unity
- Unreal
Every method is a For the platform methods the SDK exchanges a credential your platform SDK already produced; it
does not obtain one for you. Google wants an ID token, Apple an identity token, Steam a
session ticket, Facebook and Discord an access token. Facebook and Discord are login-only:
they have no Afterward, read Picking a display name? Check it’s free first — advisory, since another player can still claim it
in between:
LoginWith…Async call on FlockClient.Instance.Authentication. They throw
FlockException on failure, so wrap them in try/catch to give bad credentials or a dead network
a clean retry path. The examples run inside an async method; email, password and idToken are
your own values. With no ID, the device calls use the device ID the SDK makes on the first launch and
keeps for this install; Your first call says when to pass your own.RegisterWith…Async, so the player’s account must already exist with that account
linked to it (account linking).Sign in once. A sign-in is saved on the device and restored as the SDK starts, so check first
whether a player is signed in already (FlockClient.Instance.IsAuthenticated, once
FlockClient.IsRestoringSession is false) and sign in only when nobody is.Registering is a separate call. Logging in never creates an account, so a new player needs
RegisterWith…Async first. A successful register also signs the player in, so no login call
follows on the happy path.Registering an identity that already has an account is not an error — the call returns null
and leaves the player signed out, so follow that case with a login. A device sign-in with no
account screen logs in first, and registers only when the device has no account yet:FlockClient.Instance.CurrentPlayerId. To react wherever the sign-in came from (a
login, a register, or a sign-in restored at startup), handle FlockEvents.OnAuthenticated: its
handler takes a FlockAuthInfo (PlayerId, and Method, a FlockAuthMethod). Handle
OnAuthExpired to sign the player in again when a saved sign-in can no longer be renewed: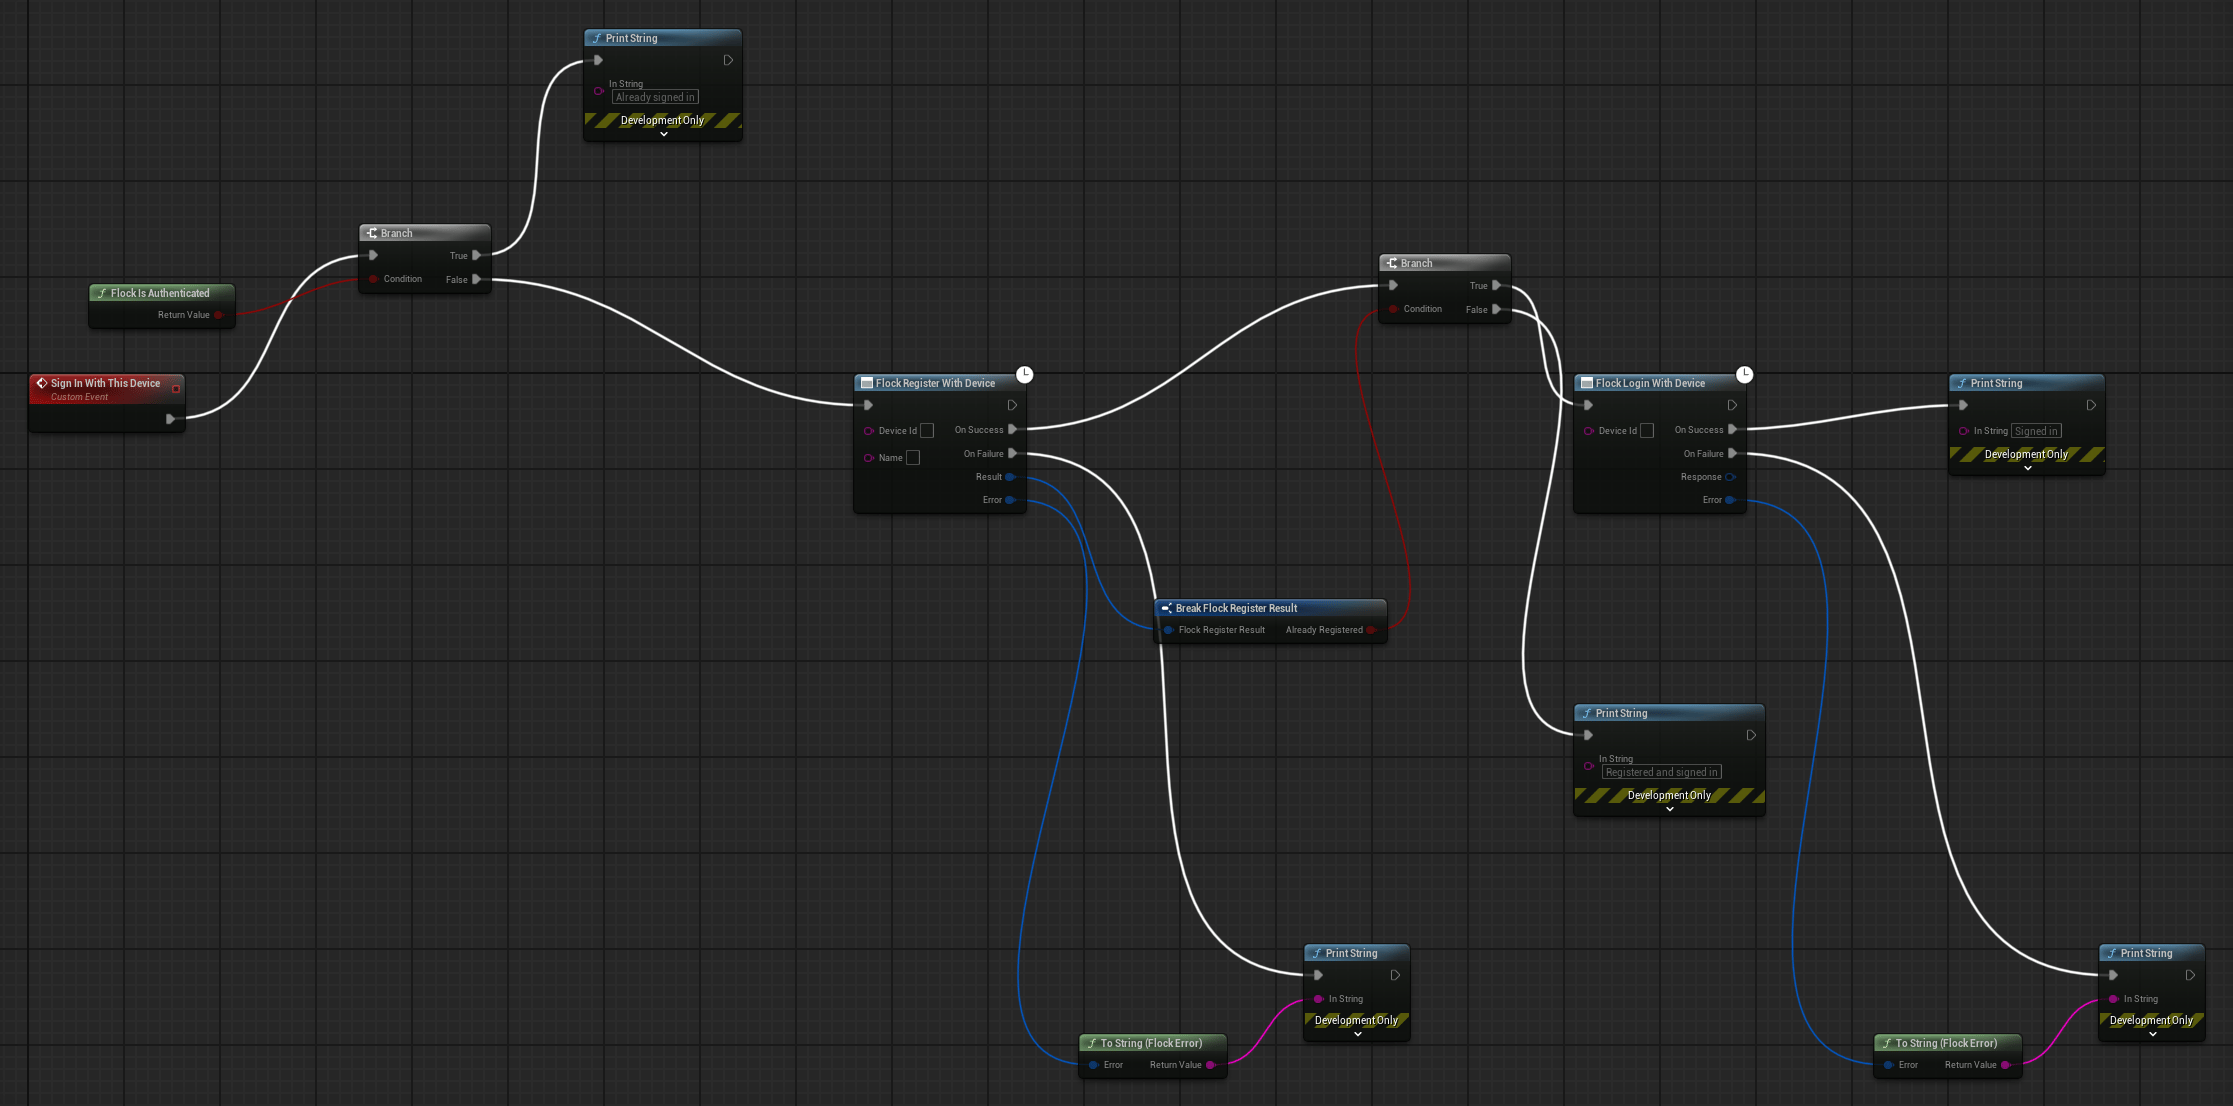
Password reset
For email/password accounts, a two-step emailed-code flow. The first call always succeeds — it never reveals whether an email is registered. Resetting works signed out: the email and the emailed code name the account, so a player who cannot sign in can still reset their password from your sign-in screen.- Unity
- Unreal
This runs inside an
async method; email, code and newPassword come from your own screens.Email verification
Optional, code-based, and always under your control — the SDK never sends verification emails on its own. Typically used while the player is signed in (their session is attached automatically), but neither call blocks on it.- Unity
- Unreal
This runs inside an
async method; code is the code the player typed from the email.Signing out
Logout clears the session on the device — the standard client sign-out. For shared devices or a
compromised session, revoking additionally kills the player’s session server-side, so a stolen
session token stops working. Shutting the SDK down is not a sign-out: the sign-in saved on the device
stays, and the next start restores the same player.
- Unity
- Unreal
This runs inside an
async method.Sessions are managed for you
Player sessions are short-lived under the hood, but the SDK refreshes them automatically — you don’t have to think about tokens or expiry. If a player needs to sign back in, the SDK raisesOnAuthExpired on its event hub (in Unreal, bind it as shown under Sign in a player).